Hyderabad Commissioner warns banks against AI-assisted cyber attacks
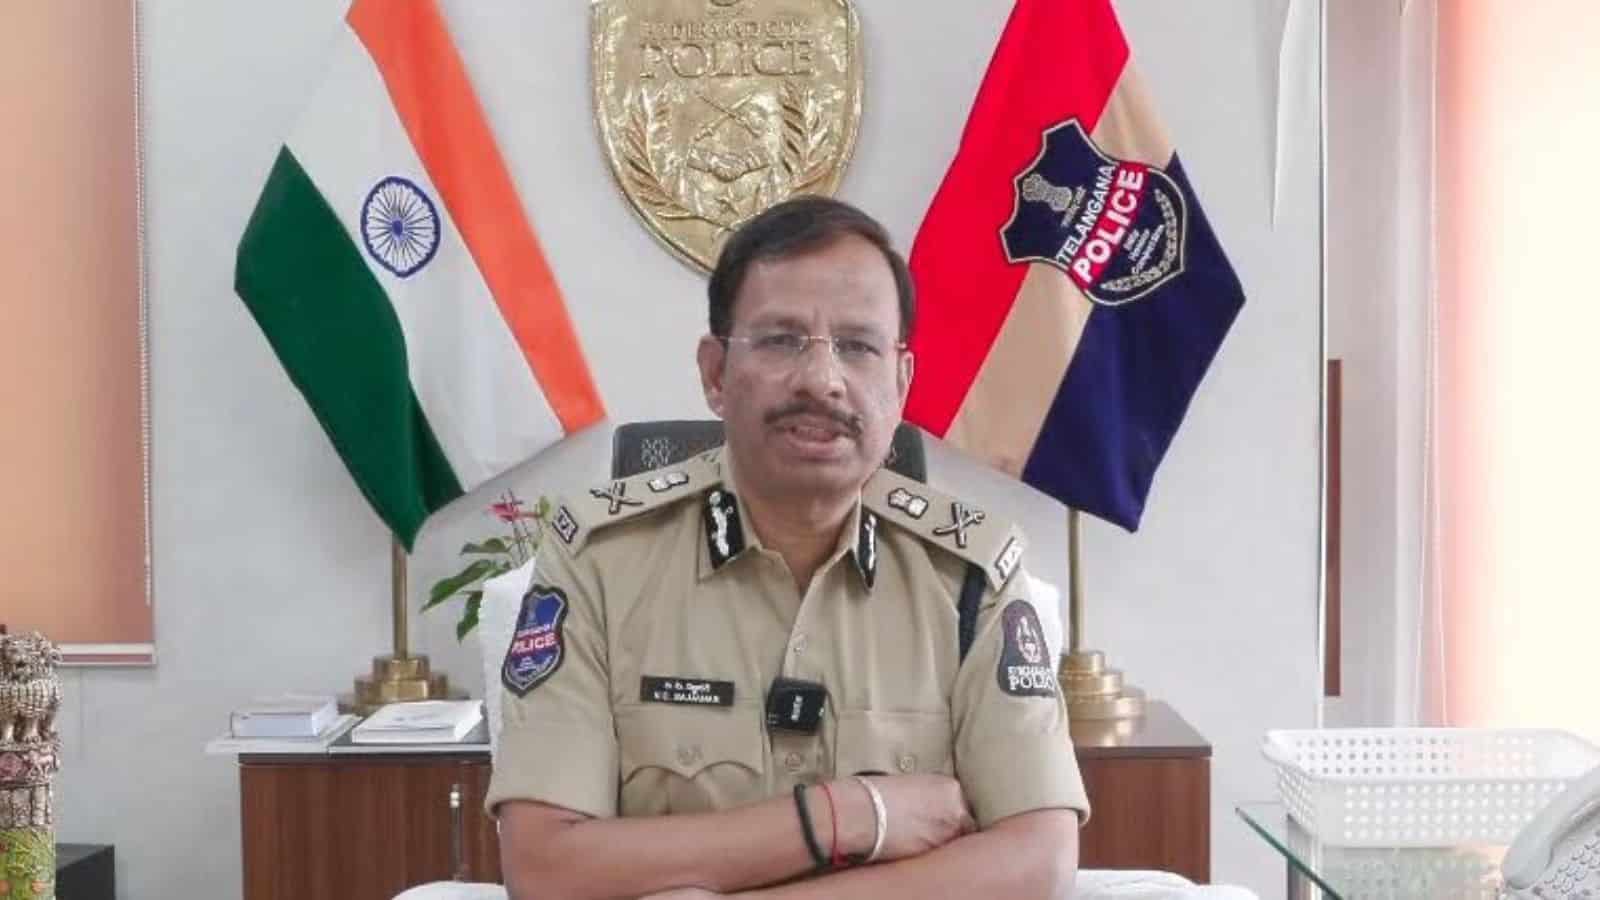
Hyderabad: Hyderabad Commissioner of Police VC Sajjanar on Monday, November 9, urged banks to strengthen their cybersecurity amid increasingly complex cybercrime incidents and evolving threats from artificial intelligence (AI)-assisted attacks.
Sajjanar said that institutions handling financial transactions of citizens and sensitive personal data must enhance their security systems to tackle the evolving nature of cyber attacks.
“Third-party systems, services and software modules handling confidential information should be treated on par with core applications. He called for stringent quality standards and security protocols to be implemented across the entire digital ecosystem,” the commissioner said in a post on X.
Increasingly complex Cyber Security incidents are being frequently reported.
— V.C. Sajjanar, IPS (@SajjanarVC_IPS) November 9, 2026
Entities handling citizen finances and data—including Banks, Financial Institutions, Quick Commerce, and Mobility Platforms—are requested to strengthen their cybersecurity systems, processes, and… https://t.co/D163AWxlWR
He emphasised that vulnerabilities in third-party applications and interconnected services could also expose sensitive information to cybercriminals, making it necessary for organisations to ensure comprehensive security checks and robust safeguards.
With citizens increasingly depending on digital platforms for financial transactions, shopping and mobility services, protecting their personal information and money has become crucial.
Strengthening cybersecurity infrastructure and improving preparedness against emerging threats are essential to safeguarding citizens’ finances, personal data and overall well-being, he added.
I 4C issues advisory
Sajjanar’s warning came after the Indian Cybercrime Coordination Centre issued a warning against AI- assisted attacks on banks. “Cybercriminals were deploying AI agents to compromise financial infrastructure, siphon off funds through payment interfaces and erase digital evidence to evade detection,” the I 4C said in a press release.
The advisory, issued jointly with the Indian Computer Emergency Response Team (CERT-In) under the Ministry of Electronics and Information Technology, has urged financial institutions to urgently implement the measures prescribed in critical-severity CERT-In advisories.
“Multi-crore unauthorised transactions through fund disbursement systems and APIs are being found in individual cases,” the advisory said, flagging a new dimension to cyber fraud in the financial sector.
According to the agencies, attackers are exploiting unpatched software, misconfigured internet-facing servers and vulnerable IT systems to infiltrate financial institutions. Customer-facing platforms and complaint-handling interfaces are also emerging as potential entry points.
Once inside these systems, hackers target automated fund disbursement mechanisms and specialised application programming interfaces (APIs) used for payments and fund transfers. The use of agentic AI frameworks enables them to execute attacks at machine speed, significantly reducing the time available to financial institutions to detect and prevent fraudulent transactions.
The stolen money is routed through ‘mule’ accounts, which criminals use to receive and transfer illicit funds across banks. The proceeds are then rapidly moved or withdrawn through Immediate Payment Service (IMPS) and National Electronic Funds Transfer (NEFT) channels.
The attackers subsequently delete transaction records and conceal their digital footprints, making forensic investigations and the recovery of funds more difficult, the advisory said.
The agencies have asked financial institutions to align their security controls with CERT-In’s May 2026 blueprint for reducing exposure to AI-assisted vulnerability exploitation, besides complying with the cybersecurity frameworks prescribed by their respective sectoral regulators.
Banks, Non-Banking Financial Companies (NBFCs) and fintech companies have also been directed to report such incidents to CERT-In within six hours of detection. Banks and NBFCs must additionally report the incidents to the Reserve Bank of India (RBI) through its DAKSH portal within the same timeframe.
Get the latest updates in Hyderabad City News, Technology, Entertainment, Sports, Politics and Top Stories on WhatsApp & Telegram by subscribing to our channels. You can also download our app for Android and iOS.
This content is published by The Siasat Daily and has not been created or edited by Hello Headlines. View original