Central Bank of India alleges hackers siphoned off Rs 13.97 crore through financial messaging system
The Central Bank of India has filed a complaint with the Mumbai police alleging that 187 unauthorised transfers moved Rs. 13.97 crore from its settlement account with the Reserve Bank of India (RBI) between October 15 and 17, according to a Hindustan Times report published on October 24.
How did the attackers access the public bank’s systems? The public sector bank’s complaint at the Nodal Cyber Police Station in Mumbai alleged that unknown persons had accessed the central Structured Financial Messaging System (SFMS) server, which is used by financial institutions, including banks and the RBI, to communicate with one another. Police have reportedly registered a case against unknown persons for cheating and personation.
The complaint states that, under the normal Real Time Gross Settlement (RTGS) process, a customer’s account is debited in the bank’s core banking system before a payment message is sent through the bank’s SFMS server to the central server operated by Indian Financial Technology and Allied Services (IFTAS) and the bank’s RBI settlement account. The complaint alleges that unknown persons gained unauthorised access to IFTAS’s central SFMS server through the bank’s SFMS server and routed the money.
While six transfers took place on October 15, 88 took place on October 16 and 93 on October 17, the Hindustan Times report states that the money was transferred to 36 different recipients. Ten accounts appeared in the SFMS database logs, but the corresponding transaction IDs were not recorded in the bank’s records. The complaint also states that the accounts listed as payers did not belong to the Central Bank of India.
Therefore, the bank’s internal team could not find the 187 transfers in its branches, internet or mobile banking channels, core banking system, RTGS settlement account or SFMS server, according to the Hindustan Times report. An unnamed police officer reportedly told the newspaper that little was known about the transactions, making it “very difficult to find how the money was siphoned off”.
As a result, the bank’s internal team could not find records of the 187 transfers in its branches, internet or mobile banking channels, core banking system, RTGS settlement account or SFMS server, according to the Hindustan Times report. An unnamed police officer reportedly told the newspaper that little was known about the transactions, making it “very difficult to find how the money was siphoned off”.
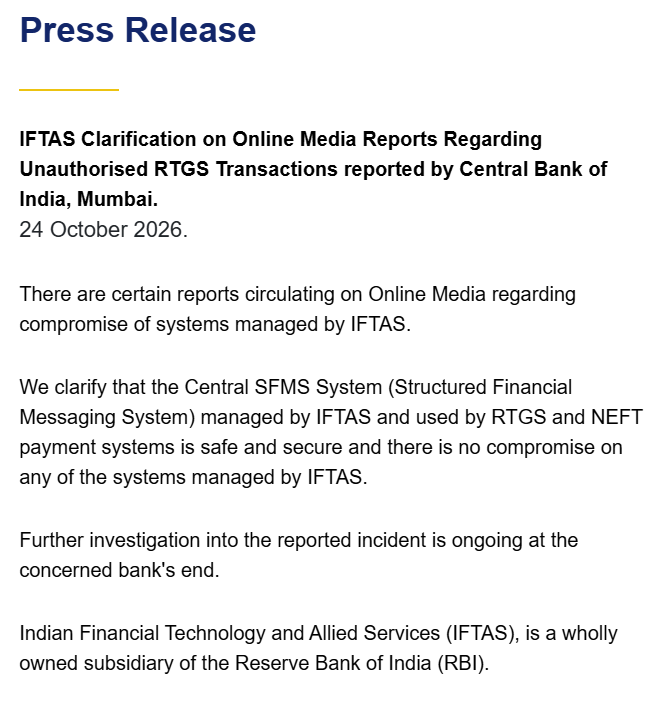
‘No compromise’; banking communications are ‘safe and secure’: SFMS is operated by IFTAS, a subsidiary of the RBI. In a press release, IFTAS claimed that “there is no compromise on any of the systems managed by IFTAS”. It also stated that SFMS, which is used for financial messaging, is “safe and secure.”
In its clarification note, the Central Bank of India said that “there was a technical issue observed in the interface environment of the localised RTGS server maintained at Bank’s end”. Without providing further details, the public sector bank claimed that no customer accounts had been affected and that its “CBS System remains entirely secure and safe.”
“RTGS Services to the customers have been fully resumed across all Channels,” the bank stated in its public response.
What is a Structured Financial Messaging System (SFMS)? SFMS is a standardised electronic messaging platform for intra-bank and inter-bank financial communication. It was developed by Tata Consultancy Services (TCS) for the Institute for Development and Research in Banking and Technology (IDRBT) under the RBI, according to a Business Standard report published when the system was launched.
The research institute that developed SFMS says the system uses Public Key Infrastructure (PKI) to secure communications and provide “Authentication, Confidentiality, Non-Repudiation and Integrity”.
“Under Public Key Infrastructure each entity will have a public key and a private key. Digital Signature will be a part of every message sent on SFMS. Digital Certificate to reside in smart card issued to authorized personnel. Smart card based access at the point of message generation will provide additional security and audit trail,” IDRBT states.
SFMS carries messages for payments processed through systems such as RTGS and the National Electronic Funds Transfer (NEFT) system. RTGS is generally used for high-value, real-time transactions, while NEFT facilitates electronic fund transfers between bank accounts.
The transfers reportedly left the bank’s RBI settlement account, but the bank could not locate corresponding transactions in its regular banking records.
The bank reportedly informed the following entities:
- Reserve Bank of India (RBI): India’s central bank and the primary regulator of the country’s banking and payment systems.
- Indian Financial Technology and Allied Services (IFTAS): An RBI subsidiary that provides critical banking infrastructure to the RBI, banks, cooperative societies and other financial institutions.
- DAKSH portal: The RBI’s platform for monitoring compliance and facilitating centralised reporting of fraud and cyber incidents.
- National Critical Information Infrastructure Protection Centre (NCIIPC): The national nodal agency responsible for protecting the country’s critical information infrastructure from cyber threats, cyberterrorism and cyberwarfare.
- Indian Computer Emergency Response Team (CERT-In): India’s nodal agency for responding to computer security incidents.
In a similar incident in 2016, hackers stole approximately US$100 million from the Bangladesh Bank. According to a DataBreachToday report, the attackers infiltrated the bank’s systems and exploited its SWIFT messaging infrastructure using malware. Like SFMS, SWIFT is a financial messaging network used by banks to communicate payment instructions.
Also Read:
- SBI confirms data of 3,897 customers exposed on dark web
- Bank of Baroda launches forensic probe after customer data appears on dark web
- Dodo Payments breach disclosure disputed by dark web listing
The post Central Bank of India alleges hackers siphoned off Rs 13.97 crore through financial messaging system appeared first on MEDIANAMA.
This content is published by MediaNama and has not been created or edited by Hello Headlines. View original